AI security agents are changing what we should expect from security software: not more alerts, but resolved risks. Instead of stopping at detection, the next security platform will investigate identity risks, remediate them when policy allows, and verify that the work is actually done.
Most security tools stop too early. They find a problem, generate an alert, and hand the rest of the work to a person.
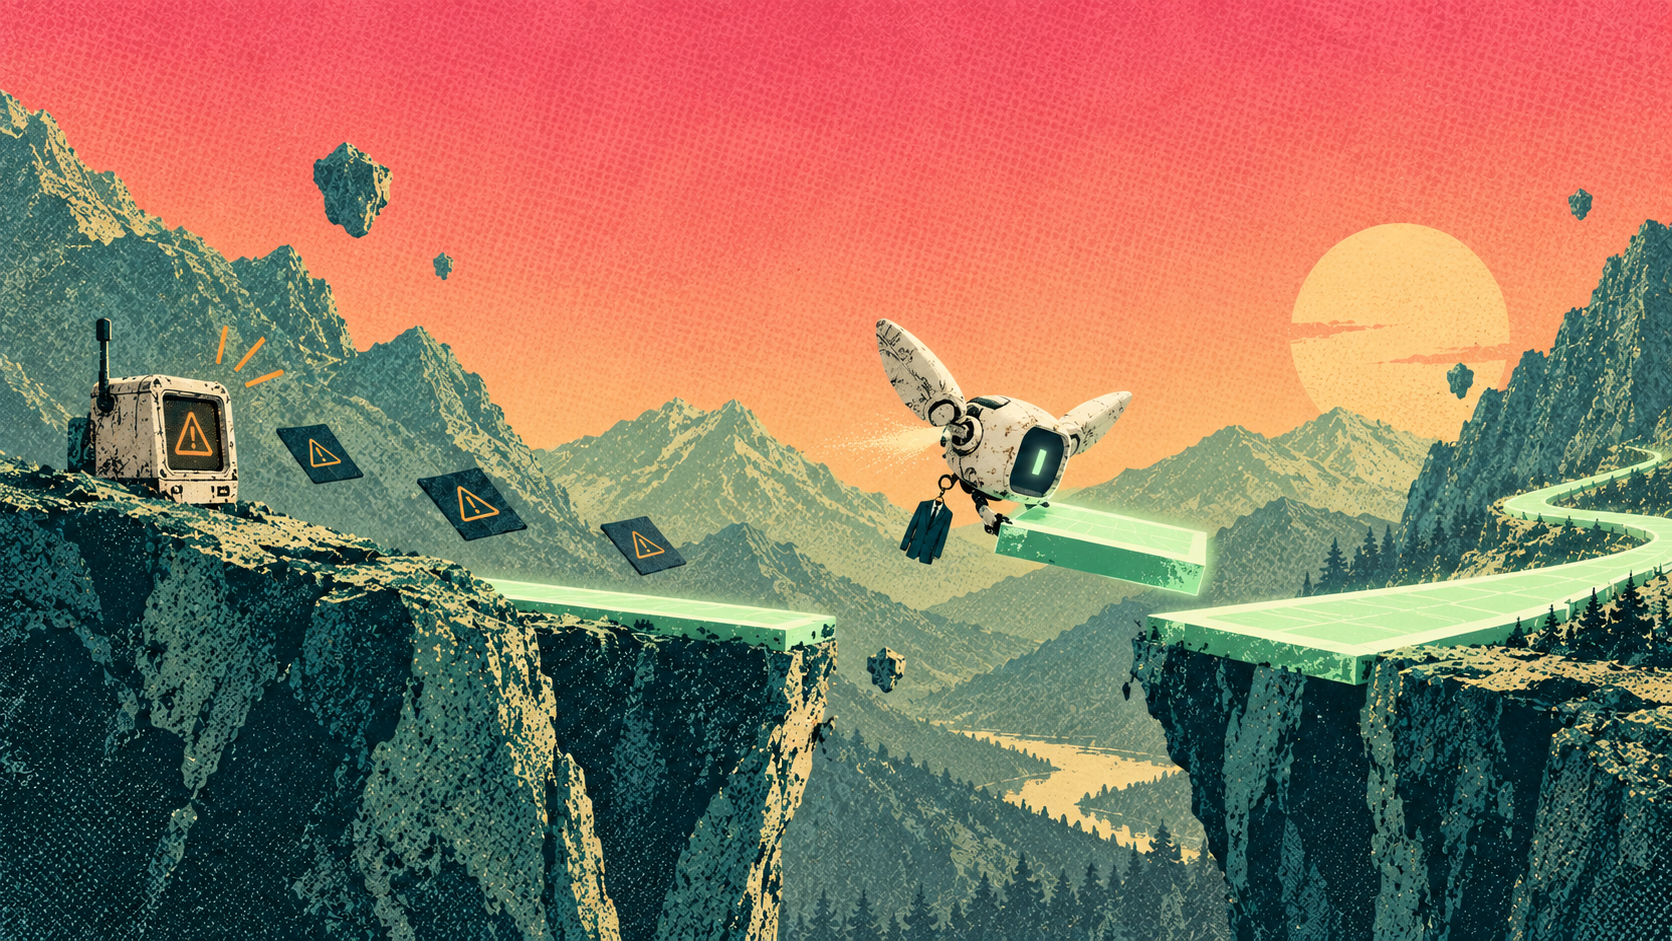
At Offroad, we are already moving beyond that model. Our agents investigate identity risks, understand the context, remediate when the evidence and policy allow it, and verify that the issue was actually resolved.
Security software should operate less like a dashboard and more like an exceptional assistant: one that deeply understands the environment across human, non-human (NHI), and AI agent identities, and brings in human judgment only when it is truly required. A recent personal experience brought this future into clear focus for me.
Key Takeaways
- Most security tools find problems and generate alerts, but people still do the work of resolving them.
- Personal AI assistants are shifting software from giving answers to taking responsibility for outcomes.
- For AI security agents, finishing the job in identity security means investigating, finding owners, applying policy, executing the change, verifying it, and preserving a recovery path.
- Full autonomy isn’t the goal. Good security agents act on clear, policy-approved cases and bring people in when judgment is required.
- Security software should be measured by how much unresolved work it removes, not how many issues it finds.
The Three-Minute Suit: What a Personal Assistant Taught Me About Software
I am going to be the best man at a wedding, and I had nothing to wear.
Work had been nonstop. By the time I realized I still needed an outfit, I did not have the time or attention to browse stores, compare suits, check sizes, and figure out what would arrive on time.
So I sent Instinct a voice message and explained what I needed and which stores I liked.
It opened a personalized dashboard with styles that matched my taste, options available in my size, and, most importantly, free returns.
Three minutes later, the suit was in my cart. It did almost everything for me.
It did not give me a list of menswear websites and send me shopping. It understood the outcome, gathered the relevant context, narrowed the options, and moved the task almost to completion.
That is a very different relationship with software.
From Answers to Responsibility: How Software Is Changing
For years, software has helped us find information and make decisions. Search gives us results, dashboards organize data, notifications tell us that something changed, and copilots help us complete individual steps.
But we are still responsible for moving the work from beginning to end.
Personal assistants are beginning to change that. Instinct is one example. OpenAI’s dots, always-on agents launched in September 2026, and the broader direction of personal assistants point to the same shift.
The important change is not simply that we can communicate with software more naturally. It is that software can begin carrying part of the responsibility.
The question changes from “What can this system tell me?” to “What part of this work can I trust it to move forward?”
Cybersecurity, and agentic security in particular, will move in the same direction.
Why Do Security Tools Stop at the Finding?
Security products have become very good at finding problems. They identify excessive access, unused permissions, unowned accounts, risky OAuth grants, suspicious activity, and service accounts with privileges they may no longer need. Then they generate an alert or open a ticket. Identity security remediation, the work of actually fixing the risk, is still left to people.
The cost of stopping there is real. In CyberArk’s 2025 State of Machine Identity Security Report, 50% of organizations reported a breach tied to compromised machine identities in the past year, and 34% still rely on manual processes to manage them.
The security team still needs to understand what happened. Why does the access exist? Who owns it? What depends on it? What could break? Which policy applies? Who needs to approve the change?
Then someone must make the change and confirm that it worked. The finding may be correct and the risk may be real, but nothing has been resolved yet.
The software found the problem, but the people inherited the work.
Imagine if Instinct had shown me 30 menswear websites with recommendations and considered the task complete. The recommendations might have been good, but I would still have been responsible for everything that mattered. In security, we have accepted that operating model for years.
Traditional security tools vs. AI security agents
- Output: Traditional tools produce alerts and tickets. AI security agents deliver resolved, verified risks.
- Context: Traditional tools show isolated findings. AI security agents connect identities, access, ownership, policy, and business context.
- Remediation: Traditional tools leave it to the security team. AI security agents remediate policy-approved cases automatically and route the rest for approval.
- Verification: Traditional tools stop when a ticket is closed. AI security agents confirm that effective access changed and preserve a recovery path.
- Human role: With traditional tools, people act as the integration layer between disconnected systems. With AI security agents, people provide judgment on sensitive or unclear cases.
- Success metric: Traditional tools count issues found. AI security agents are measured by unresolved work removed from the team.
What Does It Mean for Security Software to Finish the Job?
Finishing the job means a security platform carries a risk from detection to verified resolution. It investigates why the risk exists, finds the owner, applies policy and approvals, executes the change, verifies it worked, and preserves a recovery path. Detection alone just hands the work to people.
Example: A Service Account With Excessive Permissions
Service accounts are among the most common non-human identities (NHIs), and removing excessive service account permissions may appear simple. But that account could support a release pipeline or another critical business process.
Its original owner may have left the company. The reason for the access might exist only in an old ticket, a conversation, or the memory of the person who created it.
Before changing anything, the team needs to understand the account’s purpose, ownership, activity, dependencies, and potential impact. Only then can it decide whether the access should be removed, reduced, approved as an exception, or escalated. This is exactly the kind of work AI-powered least privilege is designed to handle.
The 7 Steps to Resolving an Identity Risk
In identity security remediation, finishing the job means carrying the issue through the full process:
- Investigate why the access exists.
- Find the owner and dependencies.
- Determine whether the access is still justified.
- Apply the organization’s policies and approval process.
- Execute the approved change.
- Verify that effective access changed.
- Preserve the evidence and a recovery path.
The final action might be one API call. Reaching a decision that can be trusted is the difficult part.
Is Full Autonomy the Goal of Security Automation?
It would be easy to frame this as a race toward complete autonomy. I do not think that is the right goal for security automation.
Some situations are clear, repeatable, and already covered by policy. They should not require a person to gather the same evidence and perform the same manual steps every time.
Other situations are sensitive or unclear. A change may affect production, interrupt an important workflow, or remove access whose purpose is not fully understood.
A good security agent should know the difference:
- When the evidence is clear and policy allows the action, it should complete the remediation and verify the result.
- When judgment is required, it should bring the right person a completed investigation, a recommendation, and the context needed to decide.
People should provide judgment. They should not have to act as the integration layer between disconnected systems.
How Offroad’s AI Security Agents Resolve Identity Risks
This is already a large part of what we do with agentic identity risk operations.
Our agents connect identities, access, activity, ownership, policies, approvals, and business context. They use that context to understand an issue before deciding how it should move forward.
- For clear, policy-approved cases, they complete the remediation and verify the result.
- When the situation is uncertain or the potential impact is significant, they involve the right person instead of making an unsupported assumption.
- Every action is recorded, and changes are verified.
- When the underlying system supports it, the previous configuration is preserved so the team has a recovery path.
Now we are taking that experience further. The goal is for security teams to spend less time managing alerts, chasing context, and moving tickets between systems. The platform should understand what needs to happen, move the work forward, and return when a real decision is required.
That is much closer to how a great assistant works, and it is why identity security needs AI agents, not more dashboards. Not another place the security team needs to monitor.
How Should Security Software Be Measured?
Security products are often measured by how many issues they identify. That tells us something, but not enough. We should also ask:
- How many issues were investigated?
- How many reached the correct owner?
- How many approved actions were completed?
- How many changes were verified?
- Most importantly, how much unresolved work was removed from the security team?
An alert can be accurate while the organization remains exposed. A ticket can be closed without proving that effective access changed.
The outcome that matters is not that the system produced more security work. It is that the environment became safer.
The Expectation Has Already Changed
My experience with Instinct was a small personal example, but it showed me a much bigger shift.
Once software can understand context, move work forward, and return when a real decision is needed, a list of recommendations no longer feels like a finished product.
Security teams will develop the same expectation. They will not be satisfied with tools that find another issue, generate another alert, and add another item to the queue.
They will expect AI security agents to investigate what happened, understand the organization around it, safely take action, involve people when judgment matters, and prove that the work was completed.
That is the direction we are already taking at Offroad.
The next security platform won’t just find problems. It will finish the job.
Frequently Asked Questions
What does it mean for a security platform to “finish the job”?
It means carrying a risk from detection to verified resolution: investigating why it exists, finding the owner and dependencies, applying policy and approvals, executing the change, verifying that effective access changed, and preserving evidence and a recovery path.
What are AI security agents?
AI security agents are software agents that do security work end to end, not just flag it. In identity security, they gather context across identities, access, and ownership, then remediate policy-approved risks automatically or route uncertain ones to a person with a full investigation.
Why isn’t detection enough in identity security?
A finding can be accurate while the organization stays exposed. Until someone investigates, gets approval, makes the change, and verifies it, the risk is still there. Detection alone shifts the work to the security team.
Should security agents remediate everything automatically?
No. Agents should act autonomously on clear, repeatable, policy-approved cases, and route sensitive or uncertain cases to the right person with a completed investigation and a recommendation.
How do Offroad’s agents handle identity risks?
Offroad’s agents connect identities, access, activity, ownership, policies, approvals, and business context. They remediate clear, policy-approved cases and verify the result, escalate uncertain or high-impact cases to the right person, record every action, and preserve previous configurations where supported.
How should security teams measure their tools?
Beyond issues found, measure how many issues were investigated, reached the correct owner, had approved actions completed, and had changes verified, and ultimately how much unresolved work was removed from the team.